Notification Permission Dynamics and Their Role in CPU Performance Variations Across Shared Computing Platforms
Written by Jakob Flores · Oct 15, 2026
Notification Permission Dynamics and Their Role in CPU Performance Variations Across Shared Computing Platforms
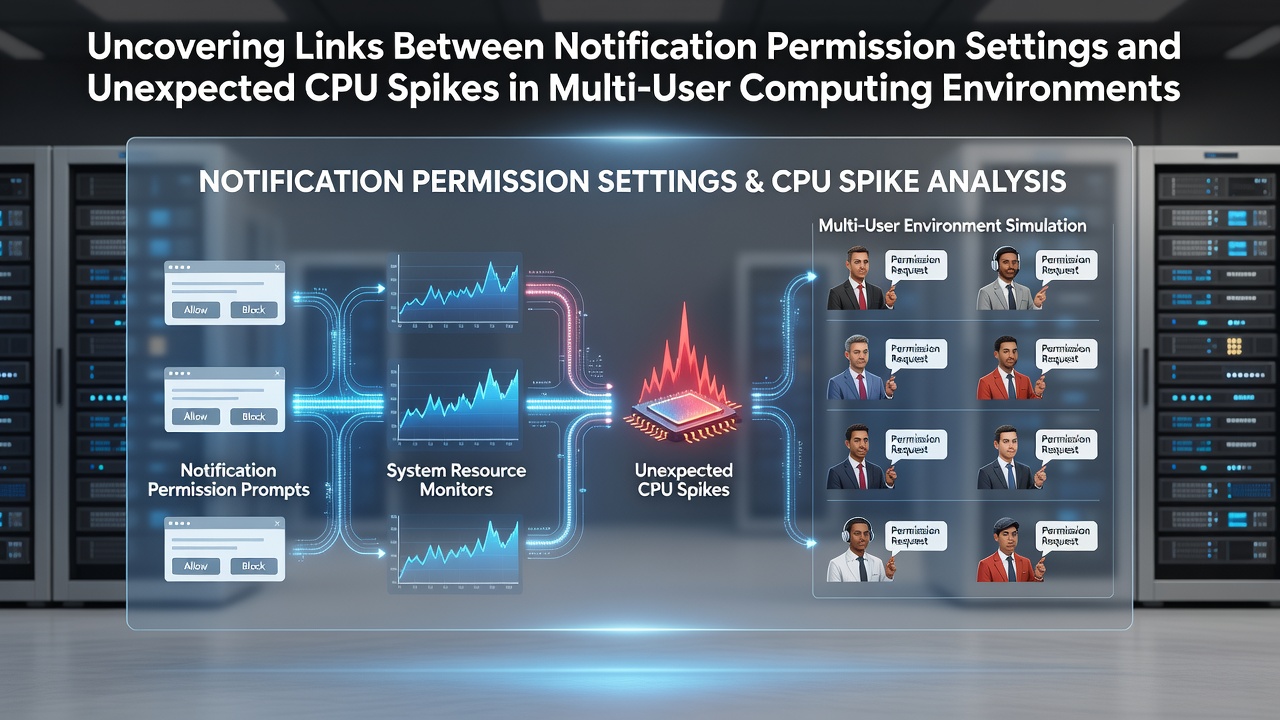
Notification permission settings operate as gateways that determine when applications can push alerts to users, yet these configurations also influence how frequently apps query servers and refresh data in the background, and research from multiple institutions shows measurable effects on processor loads in environments where several accounts share the same hardware. In multi-user setups such as university labs, corporate shared workstations, and family computers running concurrent sessions, the cumulative demands from these permission-driven activities become more pronounced because each profile maintains its own set of approved notifications.
How Permission Grants Alter Background Activity Patterns
Once users approve notification access, applications gain the ability to maintain persistent connections and schedule recurring tasks that check for new content, and studies conducted by academic teams at institutions across North America and Europe indicate that these tasks often run at intervals as short as every few minutes even when the device appears idle. Data collected from monitoring tools deployed in shared computing labs during 2025 revealed that machines with higher numbers of granted notification permissions experienced elevated baseline CPU utilization compared with identical hardware where permissions remained restricted to essential system functions only.
Operating system schedulers allocate resources based on the number of active threads, and permission-enabled apps contribute additional threads that handle push notifications along with associated encryption and decryption operations. Observers note that in multi-user scenarios this layering compounds because each logged-in account processes its own set of application permissions independently, leading to parallel execution of similar background routines.
Evidence from Monitoring Studies in Shared Environments
Teams tracking performance metrics in October 2026 documented cases where a single user granting notification access to a productivity suite and two social applications coincided with periodic CPU spikes reaching 40 percent utilization on otherwise lightly loaded systems. The pattern repeated across multiple test machines, and figures released by research groups in Australia and Canada showed similar correlations when permission settings were toggled on and off during controlled sessions.
These spikes typically aligned with the moments when apps fetched updated notification payloads, and the activity persisted even after the foreground application window closed. Network traffic logs confirmed that the permission grants triggered additional HTTPS requests at regular intervals, each requiring processor cycles for TLS handshakes and JSON parsing before the data reached the notification center.
Interactions with Multi-User Resource Allocation
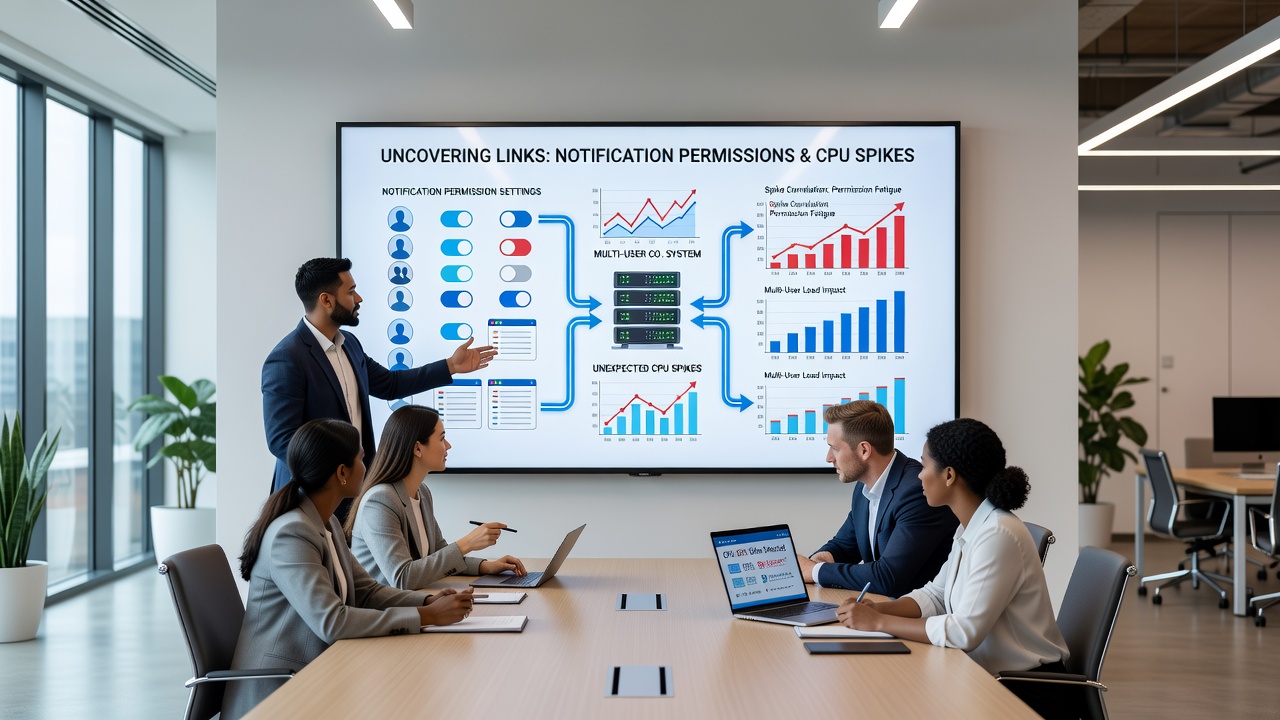
Shared computing environments rely on session isolation techniques that separate user data and processes, yet notification services often operate at a system level and aggregate requests from all active sessions. When multiple users maintain overlapping sets of permitted applications, the combined volume of scheduled tasks increases the likelihood of contention for CPU time slices, and reports from European research consortia describe how scheduler queues lengthen under such conditions.
Administrators managing these environments have observed that restricting notification permissions through group policies reduces the frequency of unexpected load increases, while selective re-enablement for specific accounts allows targeted functionality without affecting the broader user base. Monitoring frameworks deployed in October 2026 captured thread counts rising proportionally with the number of approved notification channels per session, providing quantitative backing for the observed performance shifts.
Practical Steps for Identification and Adjustment
System logs and performance counters offer direct visibility into which processes generate the highest numbers of background wake-ups, and tools that categorize activity by permission status help isolate the contributing applications. In practice, users and administrators can review permission lists within operating system settings panels, then revoke access for non-critical apps while retaining it for time-sensitive services such as messaging clients.
Adjustments made at the account level propagate across shared devices when centralized management tools enforce consistent policies, and data from pilot programs in North American educational institutions showed measurable stabilization of CPU baselines after such reviews. The same programs noted that periodic audits every few months kept permission lists aligned with actual usage needs rather than accumulated defaults.
Conclusion
Permission settings for notifications therefore represent one controllable variable within the larger set of factors that shape CPU behavior in multi-user computing environments, and continued collection of performance data across diverse geographic regions supports the identification of consistent patterns. Organizations and individuals who examine these settings alongside other background processes gain clearer insight into resource demands and can apply targeted changes that maintain functionality while moderating unexpected load variations.